TL;DR

Get smart everyday buys delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
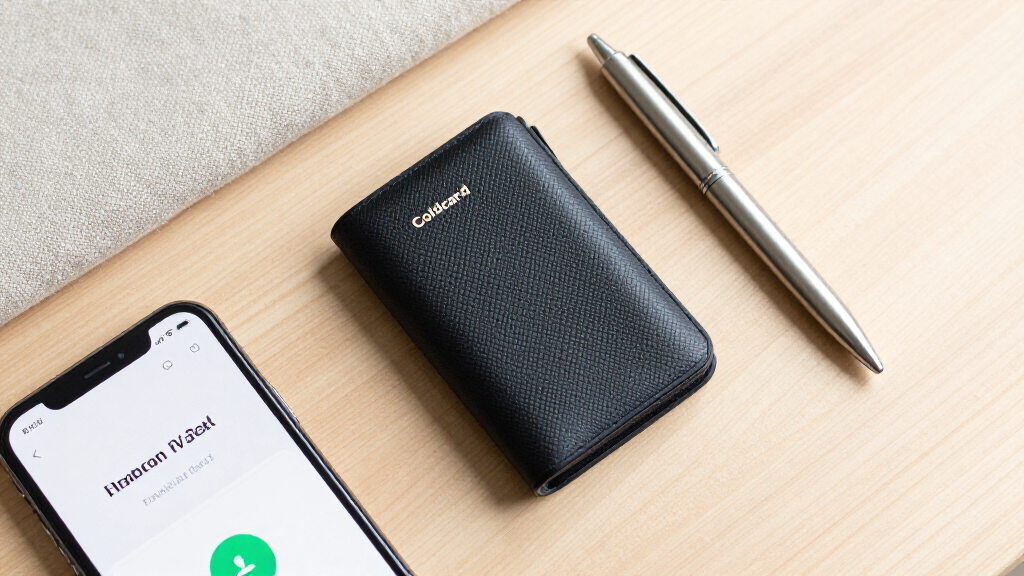
The Coldcard hardware wallet experienced a security flaw in 2021 that reduced seed entropy, enabling large-scale theft in 2023. While AI tools may have helped identify the vulnerability, there is no confirmed evidence that AI directly caused or discovered the flaw.
Recent large-scale thefts of Bitcoin from Coldcard hardware wallets, totaling over $70 million, are linked to a firmware flaw introduced in 2021. You can learn more about the best AI-powered devices in our latest guide. While some speculate that artificial intelligence tools may have played a role in discovering the vulnerability, there is no confirmed evidence of AI involvement in the attack itself. For more on AI applications in security, see AI in cybersecurity.
The security flaw stemmed from a firmware update in March 2021, which caused Coldcard devices to generate seeds with significantly reduced entropy—about 40 bits instead of the intended 128. This made the private keys vulnerable to brute-force attacks, allowing an attacker to regenerate and check potential keys on a computer, leading to the theft of over 1,800 BTC in July 2023.
While a widely circulated claim suggests that an AI model called Kimi K3, released shortly before the theft, might have identified the vulnerability, experts emphasize that there is no concrete evidence linking AI to the discovery. The attack’s pattern indicates an automated, precomputed operation rather than a novel AI-driven exploit. Coinkite, the manufacturer of Coldcard, stated it cannot confirm how the flaw was discovered, only that AI tools could have been involved in reading the firmware.
Implications of AI in Security Vulnerability Detection
This incident highlights both the potential and the limitations of artificial intelligence in cybersecurity. While AI tools can assist in analyzing code and identifying weaknesses, they are not infallible and do not replace traditional security audits. The fact that the firmware flaw was not caught despite an AI review underscores the ongoing challenges in securing hardware devices against sophisticated attacks.
For the broader community, this raises questions about reliance on AI for safety-critical assessments and the importance of layered security approaches. It also emphasizes the need for transparency and verification in claims about AI capabilities in security contexts.
hardware wallet with seed entropy protection
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Background on Coldcard Vulnerability and AI Claims
The Coldcard hardware wallet, produced by Canadian firm Coinkite, is designed for secure offline storage of Bitcoin. The firmware update in March 2021 introduced a bug that compromised seed unpredictability, which was only discovered through technical analysis months later. In July 2023, attackers exploited this flaw to drain wallets, with the pattern suggesting automated, large-scale operations.
Shortly after the theft, a pseudonymous account claimed that AI model Kimi K3 had identified the vulnerability, citing the timing of its release and the attack. Experts, however, note that the flaw was already publicly known, and AI’s role in discovering it remains unproven. Coinkite’s own review, conducted weeks before the attack, failed to detect the bug, illustrating AI’s current limitations in security testing.
Bitcoin cold storage hardware wallet
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Unconfirmed Role of AI in Exploiting or Detecting the Flaw
There is no verified evidence that artificial intelligence directly discovered the Coldcard firmware flaw or was used in the attack process. The claim linking Kimi K3 to the vulnerability remains speculative, and experts caution against overestimating AI’s current security detection abilities. The actual discovery method of the flaw is still unknown.
AI cybersecurity tools for hardware security
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Future Steps in Coldcard Security and AI’s Role
Further investigations are expected to clarify how the firmware flaw was identified and exploited. Coinkite may review and enhance its security protocols, including more rigorous firmware audits. The incident also underscores the need for ongoing research into AI’s capabilities and limitations in cybersecurity, with potential developments in automated vulnerability detection tools.
As an affiliate, we earn on qualifying purchases.
Key Questions
Did AI directly cause the Coldcard firmware flaw?
There is no confirmed evidence that artificial intelligence caused or discovered the flaw. The link to AI remains speculative, and the flaw was likely identified through traditional security analysis or brute-force methods.
Could AI have helped identify the vulnerability earlier?
While AI tools can assist in analyzing code, the Coldcard firmware flaw was not detected in prior reviews, including one conducted by Coinkite before the attack. AI’s role in vulnerability detection is still limited and not yet reliable enough for critical hardware security assessments.
What does this mean for hardware wallet security?
The incident highlights the importance of thorough security testing and the risks of firmware bugs. It also shows that relying solely on AI for security reviews is insufficient, emphasizing the need for layered, manual, and automated testing approaches.
Will AI be more involved in future security audits?
AI is expected to become part of security workflows, but experts stress it will complement rather than replace traditional methods. Ongoing research aims to improve AI’s effectiveness in detecting vulnerabilities without overestimating its current capabilities.
Source: ThorstenMeyerAI.com
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.