TL;DR

Get smart everyday buys delivered free with Prime
- Fast, free delivery on millions of items
- Prime Video, Amazon Music and more included
- Member-only deals all year
Bottomline risk and fraud officer Katie Elliott told PYMNTS that AI is helping fraudsters make B2B payment attacks broader and faster, while manual verification remains costly for finance teams. She argued that companies need multiple signals to assess payment requests, with AI handling routine activity and people reviewing anomalies. The report does not provide new fraud statistics or details of a specific incident.
AI is making B2B fraud attempts easier to scale, while finance teams still face the expense of checking payment instructions and supplier identities, Bottomline senior risk and fraud officer Katie Elliott told PYMNTS. Her account points to a shift in fraud prevention: companies may need verification systems that combine multiple signals and reserve human review for unusual payments, rather than relying on manual checks for every transaction.
Elliott said criminals are using available AI tools to make attacks “bigger, broader, faster.” She described a change from more targeted activity toward mass phishing and spamming. The interview did not identify a particular company targeted by such an attack or give figures showing how much fraud has increased.
The pressure on payment teams is partly about timing. Elliott said that after a payment is authorized, funds can move quickly and recipients may withdraw them as soon as possible. That makes checking the recipient and payment request before funds are sent more important than depending on recovery afterward, she said.
She recommended weighing multiple indicators rather than trusting a single data point. These can include digital identity, phone information, email-domain history and other details that help determine whether a payment request fits the supplier’s established behavior. Elliott said obtaining third-party data and verification services can be expensive, particularly for smaller businesses.
Why Payment Checks May Need to Scale
The problem described by Elliott is a mismatch in operating costs: fraudsters can send large numbers of attempts, while businesses cannot necessarily add staff to investigate each one. If payments move quickly, a successful attempt may be difficult to reverse. That places greater weight on controls that identify a suspicious request before authorization.
One possible response, according to Elliott, is for payment networks to spread the cost of data, verification tools and expertise across more transactions. In that model, networks would offer value not only by moving funds but also by supporting shared verification capabilities that an individual accounts payable team might find too costly to build alone. The interview presents this as a potential direction, not a confirmed industry-wide change or a specific product announcement.
The approach also changes how people are used. Rather than subjecting every payment to the same manual scrutiny, teams could use automated systems for routine activity and send exceptions to staff. That may help focus limited attention on moments when supplier trust is in doubt, though the source does not quantify possible savings or show that any particular system prevents fraud.
Products Worth Considering
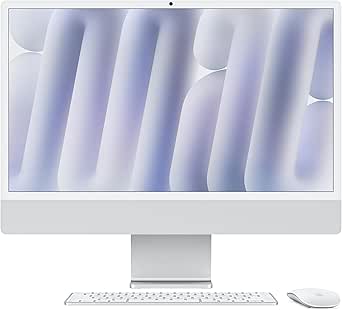
Apple iMac 2024 All-in-One Desktop with M4 Chip, 24‑inch Retina Display, 16GB Unified Memory, 256GB SSD, Silver

Apple iPad Air (2025) 13‑inch Wi‑Fi 256 GB – Space Gray (M3 chip)

Dell UltraSharp U2725QE 27-Inch 4K UHD IPS Black Monitor
As an affiliate, we earn on qualifying purchases.
From Supplier Onboarding to Ongoing Checks
Businesses commonly verify suppliers during onboarding and maintain payment controls within accounts payable. Elliott’s concern is that a successful initial check may not be enough if attackers can create convincing identities or later impersonate a legitimate supplier. The interview frames identity verification as a continuing payment concern, rather than a one-time administrative step.
She described several changes that could prompt human review: bank-account or payment-instruction changes, a sudden increase in transaction speed, or an unusually large request. As an example, she said that a supplier normally paid a consistent amount but suddenly requesting three times as much should be sent for human approval. The example illustrates a proposed control, not a report of a documented fraud case.
The report is based on Elliott’s comments during a PYMNTS discussion associated with the B2B Payments Event 2026. It offers an industry practitioner’s assessment of risk and possible controls; it is not a survey of businesses, a measured study of fraud losses or an announcement of new regulatory requirements.
““They are using the technology that’s out there, the AI, every tool available to them in order to make their attempts bigger, broader, faster.””
— Katie Elliott, senior risk and fraud officer at Bottomline, speaking to PYMNTS
Fraud Scale and Controls Remain Unmeasured
The interview does not provide measured rates of AI-enabled B2B fraud, loss totals or a comparison with earlier periods. It also does not quantify how often supplier impersonation succeeds, how quickly funds are recovered, or how much verification tools cost across businesses of different sizes.
It remains unclear how widely payment networks currently provide the shared verification services Elliott described, what data those services use, and how businesses would assess their accuracy and privacy implications. The report also does not establish that automated systems can reliably distinguish every legitimate change from a fraudulent one. Elliott’s remarks are an expert’s assessment of emerging risks and possible responses, not proof that a particular fraud-prevention model works.
The practical next steps described in the interview are for finance teams to assess multiple supplier and payment signals, establish which changes should trigger review, and direct human attention toward those exceptions. Companies considering third-party verification or network services would need to evaluate their costs and how well the checks fit their payment processes.
PYMNTS pointed readers to its full interview with Elliott for further discussion of AI-driven fraud and payment controls. The source material does not announce a product launch, implementation timetable or new policy deadline. The next developments to watch are whether payment providers expand shared verification tools and whether businesses can demonstrate that automated screening and exception review reduce risk without unduly delaying legitimate payments.
Key Questions
What is the development described in the report?
A PYMNTS interview with Bottomline’s Katie Elliott describes how AI may let criminals scale B2B payment attacks while manual checks remain costly for finance teams. It discusses possible changes to verification, not a specific newly disclosed fraud incident.
What payment signals did Elliott say businesses should consider?
Elliott cited digital identity, phone information, email-domain history and other signals that can help establish whether a payment request makes sense. She advised against making a payment decision based on one piece of data alone.
When does the report say a person should review a payment?
Human review could be triggered by unusual activity, such as a change in payment instructions, a sharp rise in transaction velocity or a request that departs from a supplier’s usual payment pattern.
Does the report show that AI has increased B2B fraud by a measured amount?
No. The interview contains no fraud-rate statistics or loss comparison. It reports Elliott’s assessment that AI can make attempts broader and faster, but does not quantify the effect.
Why discuss payment networks as part of verification?
Elliott said third-party data and verification tools can be expensive for individual businesses, especially smaller ones. Payment networks could potentially spread those costs across a wider transaction base, though the interview does not detail a specific service or deployment.
Source: rss