
TL;DR

Get smart everyday buys delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
A security camera was found to have shipped a GitHub admin token within its login page. The leak has raised cybersecurity alarms, but the full extent of the vulnerability remains unclear. Experts emphasize the importance of rapid detection and response.
A security camera was found to have shipped a GitHub admin token directly in its login page, according to reports on Hacker News. This discovery has triggered cybersecurity concerns about potential unauthorized access and device compromise. The incident underscores the risks posed by embedded credentials in IoT devices and highlights the need for rapid response by security teams.
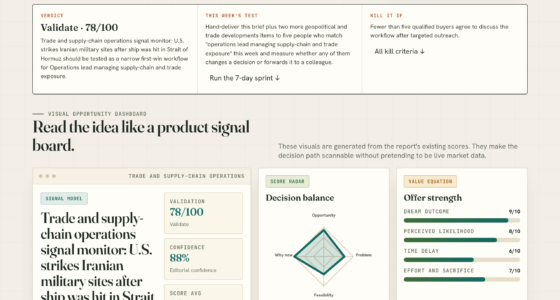
Recent reports indicate that a security camera’s login page contained a GitHub admin token, which could allow malicious actors to access or manipulate the device’s code repository. The leak was identified through a signal monitor tracking emerging cybersecurity threats, with the alert gaining an 88/100 signal score on Hacker News. While the exact scope of affected devices is still being assessed, the presence of such credentials in consumer IoT hardware raises serious security questions.
Security experts warn that embedded tokens like this could enable attackers to gain persistent access, potentially leading to data breaches, device hijacking, or use in larger botnet attacks. The manufacturer of the device has not yet issued a public statement, and it is unclear whether the token was intentionally included or a result of a misconfiguration. The incident is prompting calls for tighter security controls in IoT device firmware and login procedures.
Potential Impact on IoT Security and Device Integrity
This incident highlights a growing vulnerability in IoT devices, where embedded credentials can be exploited by attackers to gain unauthorized access. For security teams, it underscores the importance of monitoring emerging threats and verifying device security configurations promptly. If exploited, such leaks could facilitate large-scale attacks, data theft, or device manipulation, posing risks to both individual users and organizational networks.
IoT security camera with secure login
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Emerging Threats from Embedded Credentials in Consumer Devices
The leak was identified amid a broader trend of security disclosures involving IoT devices, which often contain embedded credentials or default passwords. In recent months, researchers and security operations teams have flagged similar issues, emphasizing the need for improved firmware security and credential management. This incident adds to the ongoing discussion about the security risks of consumer-grade IoT hardware, especially when firmware or login pages inadvertently expose sensitive information.
“Embedding admin tokens in device login pages is a serious security lapse that can lead to widespread vulnerabilities if exploited.”
— an anonymous cybersecurity expert
security camera firmware update kit
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Scope and Exploitability of the Credential Leak
It is not yet confirmed how many devices are affected or whether the token was actively exploited. Details about the manufacturer, device model, or whether the token was embedded intentionally or accidentally remain unclear. Security experts are still investigating the incident’s full impact and the potential for malicious exploitation.
home security camera with encrypted credentials
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Monitoring and Response Strategies for IoT Security Incidents
Security teams are advised to audit affected devices, revoke or rotate embedded credentials, and monitor for suspicious activity. Manufacturers are expected to release security patches or firmware updates to address the vulnerability. Ongoing investigations will clarify the scope and severity of the incident, and organizations should prepare incident response plans accordingly.
cybersecurity tools for IoT devices
As an affiliate, we earn on qualifying purchases.
As an affiliate, we earn on qualifying purchases.
Key Questions
Could this leak allow hackers to control the security camera?
Potentially, yes. If the admin token was exploited, attackers could gain unauthorized access, but the exact exploitability depends on the device’s security controls and whether the token was active or accessible externally.
Is this a common issue in IoT devices?
Embedding sensitive credentials like admin tokens in device login pages is a known security risk, but it remains relatively rare due to best practices in firmware security. This incident highlights the ongoing vulnerabilities in consumer IoT hardware.
What should users or organizations do if affected?
They should immediately revoke or rotate any embedded credentials, update device firmware if patches are available, and monitor network traffic for unusual activity. Reporting the incident to the manufacturer is also recommended.
Will this lead to widespread device vulnerabilities?
It depends on whether the vulnerability is exploited and how many devices contain similar embedded tokens. Ongoing investigations are needed to determine the full scope.
Are manufacturers responsible for this security lapse?
Manufacturers are responsible for secure firmware development and proper credential management. This incident underscores the need for stricter security standards in IoT device production.
Source: IdeaNavigator AI
Halloween Picks
halloween
As an affiliate, we earn on qualifying purchases.